Connect through proxies
Connect SFTPPlus MFT to cloud services through HTTP or SOCKS5 proxies, and publish its web interfaces behind a reverse proxy or application gateway.
Continue reading
This is a subset of our news articles, filtered by tag.
Connect SFTPPlus MFT to cloud services through HTTP or SOCKS5 proxies, and publish its web interfaces behind a reverse proxy or application gateway.
Bind partner accounts and groups to their expected source networks, adding identity-aware access control beyond a network firewall.
Use native TOTP or external identity providers to protect Web Client, SFTP, FTPS, and administrator logins with more than a password.
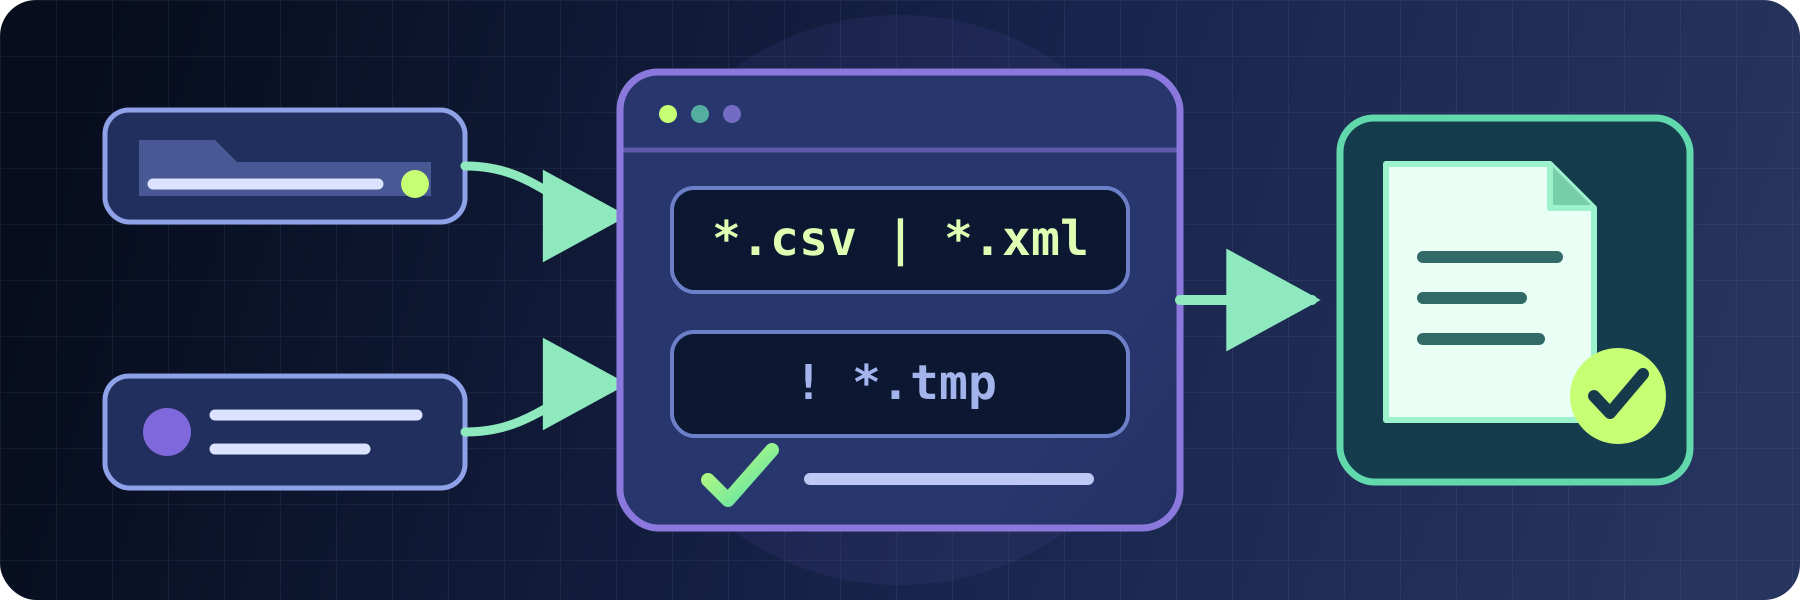
Use readable glob patterns or precise regular expressions to select and exclude files, events, and other values across SFTPPlus MFT.
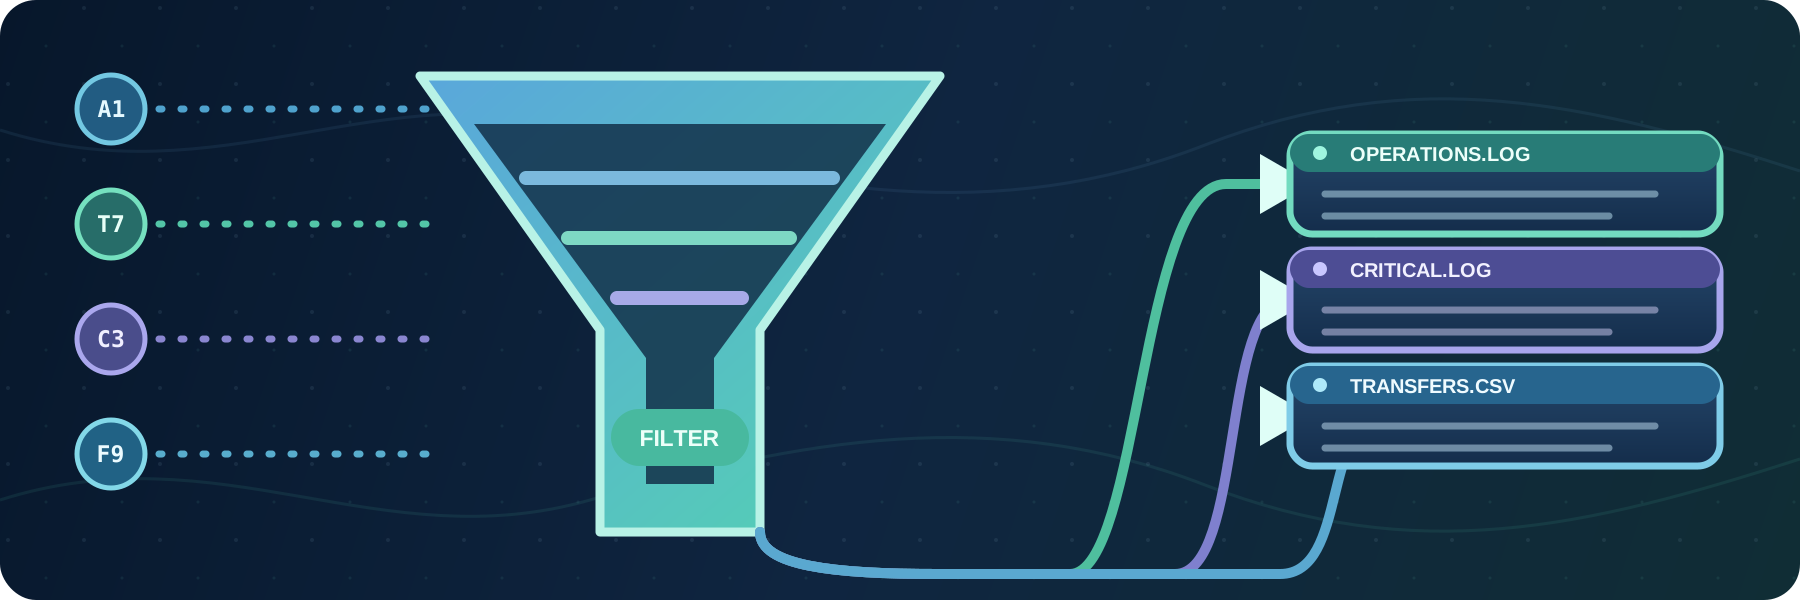
Write filtered audit events to text or CSV files, with independent formats, locations, rotation schedules, and retention limits.

Protect file transfer services with explicit source IP rules and automatic temporary blocks for repeated failed authentication attempts.
Choose whether SFTPPlus MFT fails, skips, replaces, or renames files when the destination already contains the same name.
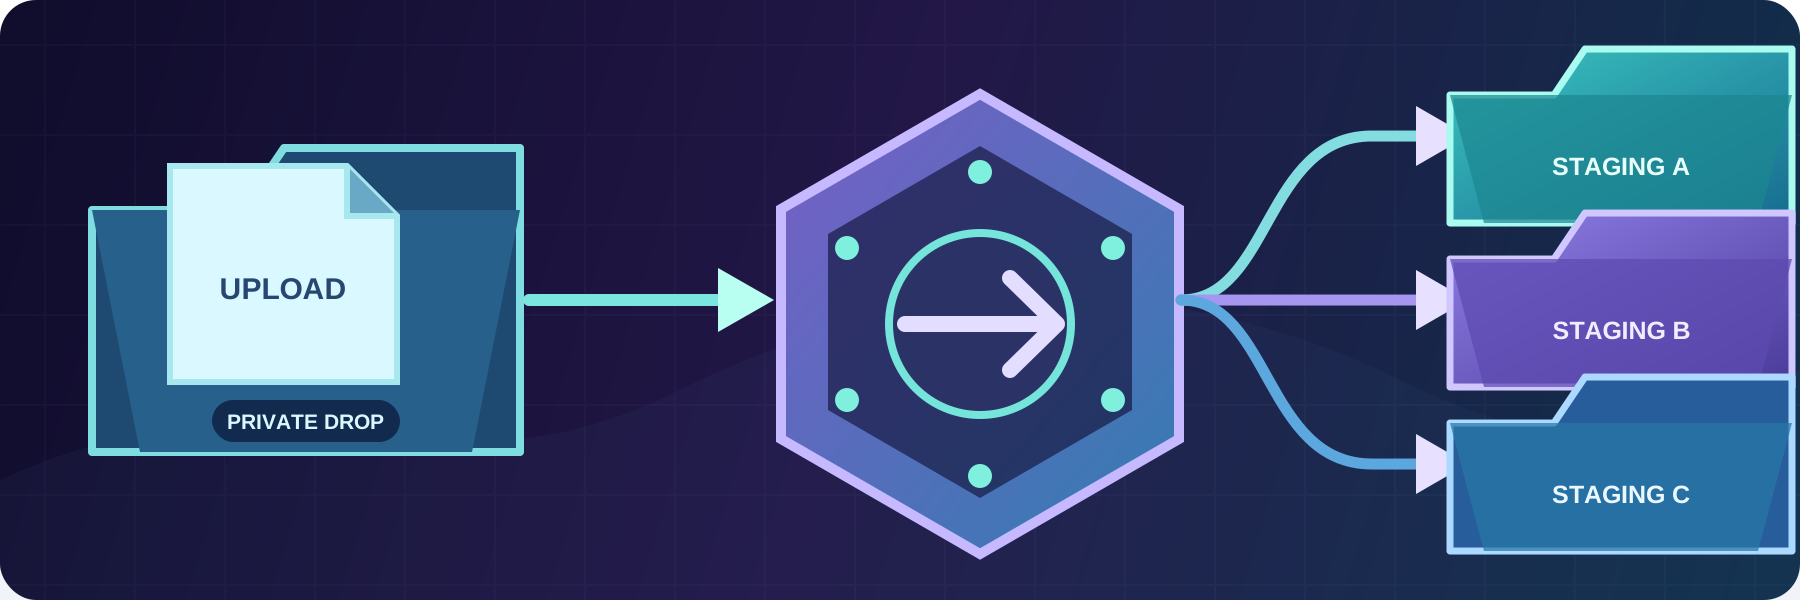
Move, copy, rename, or remove files after a transfer without maintaining custom pre-transfer or post-transfer scripts.
Call specialized or legacy tools from SFTPPlus MFT events, pass event details to them, and reuse their text or structured JSON results.

Connect SFTPPlus MFT to existing applications through HTTP APIs, webhooks, or the separately licensed SFTPPlus SDK.